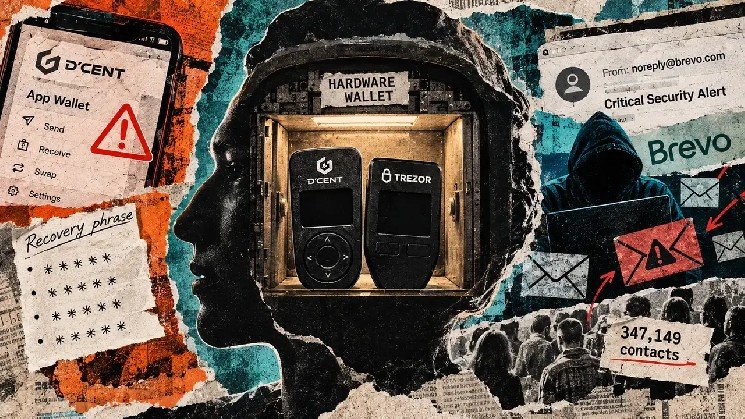
Two wallet incidents this week exposed a growing weakness in crypto self-custody: the systems surrounding hardware devices.
D’CENT, a popular hardware wallet in South Korea, said it is investigating unauthorized transfers from some users of its software-based App Wallet, while Trezor, another crypto hardware firm, disclosed that attackers exported 347,149 customer email contacts after breaching third-party marketing provider Brevo.
Neither company has reported a compromise of its hardware-wallet security.
Yet both incidents created routes to the same prize: the recovery phrase that can reconstruct a wallet and control its assets.
D’CENT phrase reuse pulls hardware assets into software risk
D’CENT’s investigation shows how moving a recovery phrase into software can extend risk beyond the device where the wallet was originally created.
The company first received reports of unauthorized transfers on Sept. 16 and found that most affected users were operating its App Wallet, which stores or imports keys on a phone. D’CENT has not confirmed a compromise affecting its hardware products and continues to investigate the cause and total scope of the transfers.
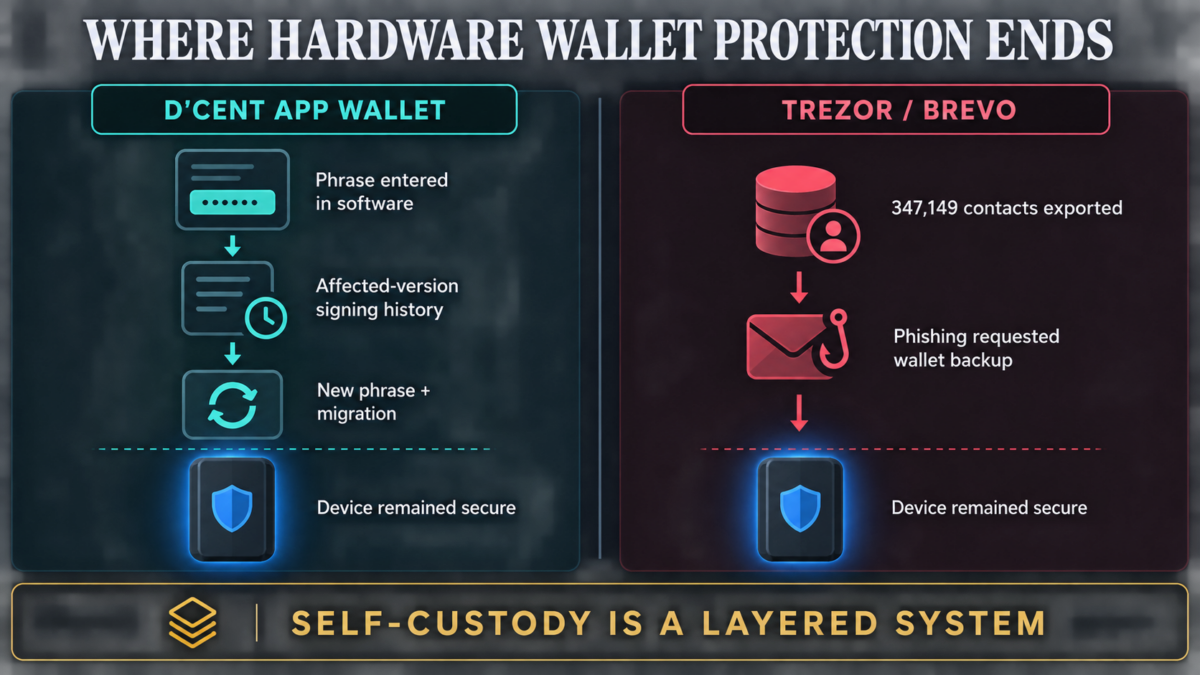
Its current criteria focus on wallets whose recovery phrases were entered into the App Wallet and that had transaction-signing history on versions earlier than 8.1.0, released Nov. 5, 2025. The potential exposure spans Bitcoin, Ethereum, XRP Ledger, Tron, and other EVM-compatible networks.
That creates a potential crossover for hardware users. A recovery phrase generated on a D’CENT device can reconstruct the same private keys elsewhere if the user later imports those words into the software wallet. D’CENT said connecting a hardware device to its app normally does not transfer the recovery phrase onto the phone; manually importing the phrase into App Wallet does.
The company is advising users who meet its criteria to update the app before signing another transaction, create a wallet backed by a new recovery phrase, and transfer affected assets rather than restoring the old phrase onto another device.
D’CENT is also working with exchanges, law enforcement and blockchain investigators to trace and potentially freeze stolen assets.
Trezor breach turns customer data into an attack surface
Trezor’s incident began further from the wallet itself, showing how information about who owns a device can become useful infrastructure for attackers.
Brevo said an attacker exploited a flaw in its SAML single-sign-on implementation to reach 138 customer accounts. Contacts were exported from 43 accounts, while six were used to send phishing emails through legitimate customer infrastructure. The messages therefore passed normal email-authentication checks and appeared to originate from trusted systems.
For Trezor, the breach exposed 347,149 marketing email contacts. Attackers sent a message claiming a critical hardware vulnerability and requiring customers to download an application that then requested their wallet backup. About 2,500 recipients reached the malicious domain before Trezor disabled it.
Trezor said clicking the link alone did not expose funds. However, the risk arose if a user entered the backup into the malicious application, allowing an attacker to recreate the wallet elsewhere.
The exported email list creates a longer-lived problem even after the first phishing domain has disappeared. Verified contact details for hardware-wallet users can be reused in follow-up campaigns tailored around future security alerts, software updates, or support requests.
Trezor had already confronted a related exposure in August when a shipping-provider incident disclosed customer identity and order information. The company said that breach exposed phone numbers and shipping addresses while leaving its wallets unaffected.
The two events show how vendors outside a hardware maker’s direct infrastructure can supply attackers with information needed to identify likely crypto holders and build more convincing approaches.
Wallet makers face a wider security burden
The incidents are likely to increase pressure on wallet companies to treat customer databases and software workflows as part of the same security program as their devices.
Trezor said it has suspended its Brevo account and is reviewing vendor relationships and security requirements following the breach. Brevo closed the SSO route used by the attacker, reset active sessions, and said it was deploying a permanent fix that restricts authentication to the organization that owns each SSO configuration.
D’CENT, meanwhile, said it is adding safeguards and pre-release verification procedures while its investigation continues. Its immediate challenge is determining the full set of affected addresses and whether assets already moved can be recovered through exchanges or law enforcement.
Both companies still depend on users keeping recovery phrases offline. Once those words are entered into compromised software or surrendered through phishing, the attacker no longer needs to defeat the hardware device.
That shifts part of the competitive burden for wallet makers beyond secure chips and signing architecture.
Companies selling self-custody products will increasingly have to show how they limit retained customer data, vet outside vendors, and design companion software so a compromise elsewhere in the stack doesn't provide another path to the keys their hardware was built to protect.